

Last updated on
Privacy and data
Your company's Frontierz data is kept within its own organisation account. This includes users, AI Fellows, Learning Paths, conversations, analytics, uploaded reference material, and settings.
This page explains what information Frontierz uses during learning and conversations, who can access it, and which account-specific details to confirm with the Frontierz team.
Uploaded knowledge
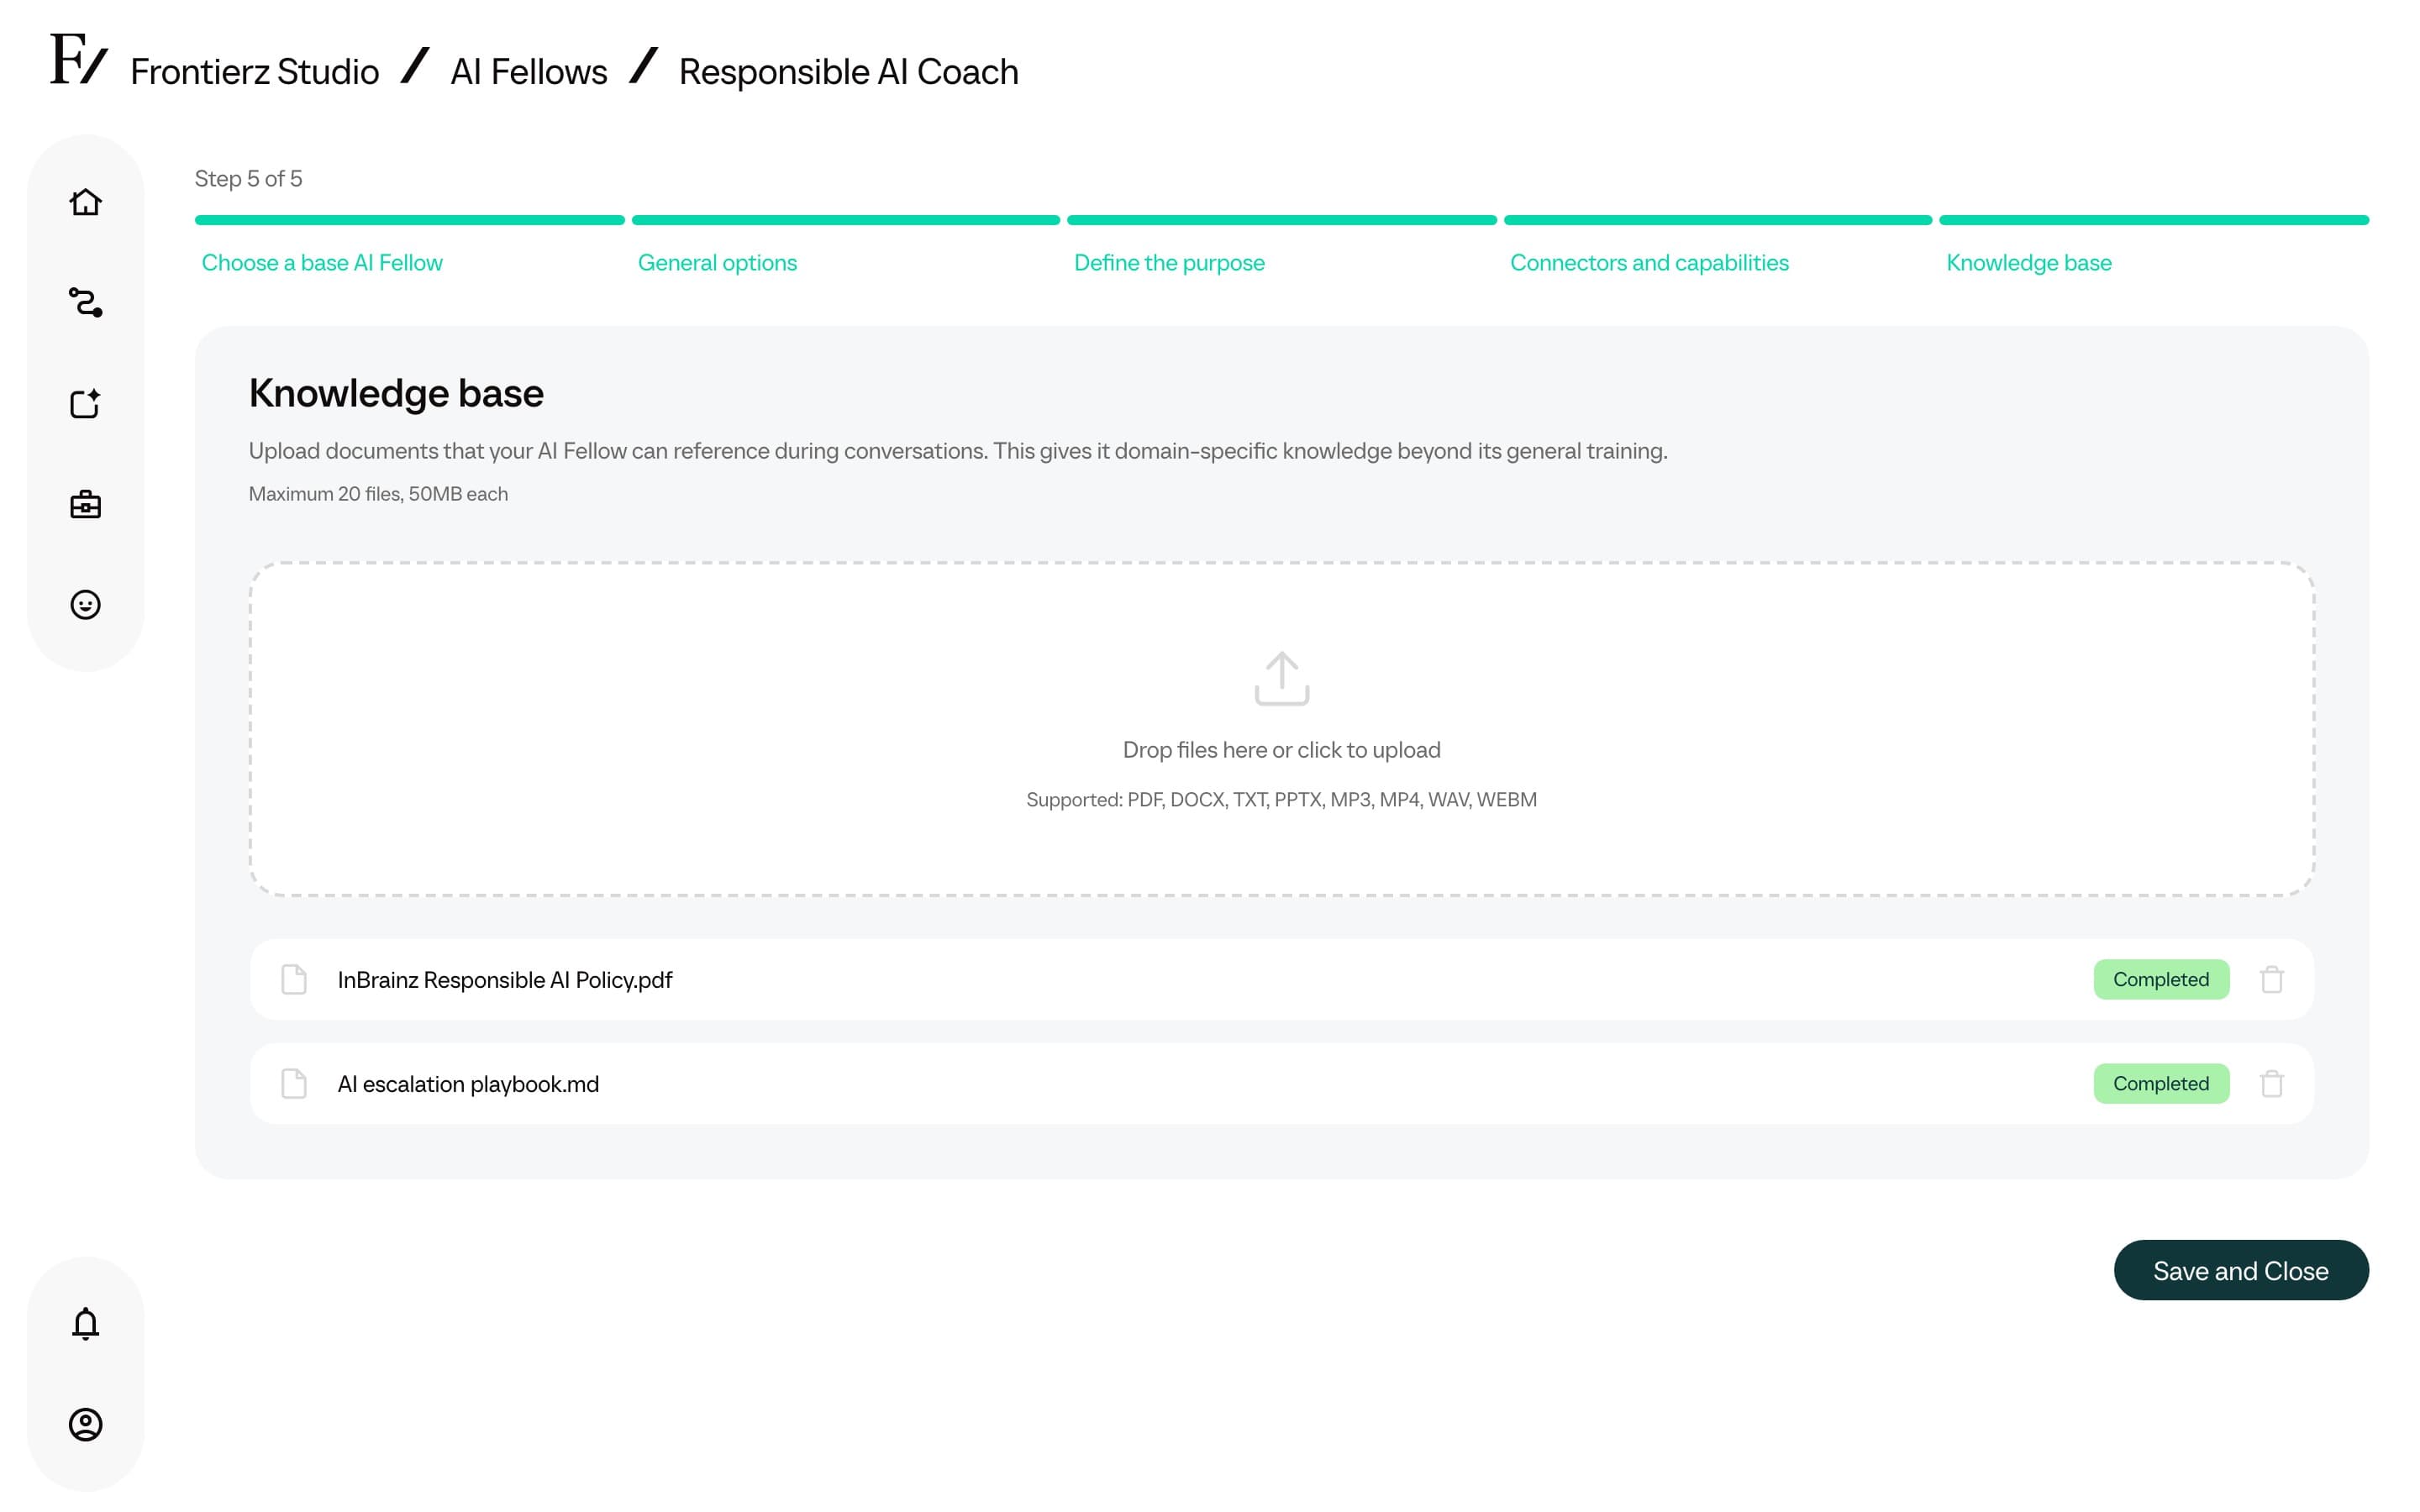
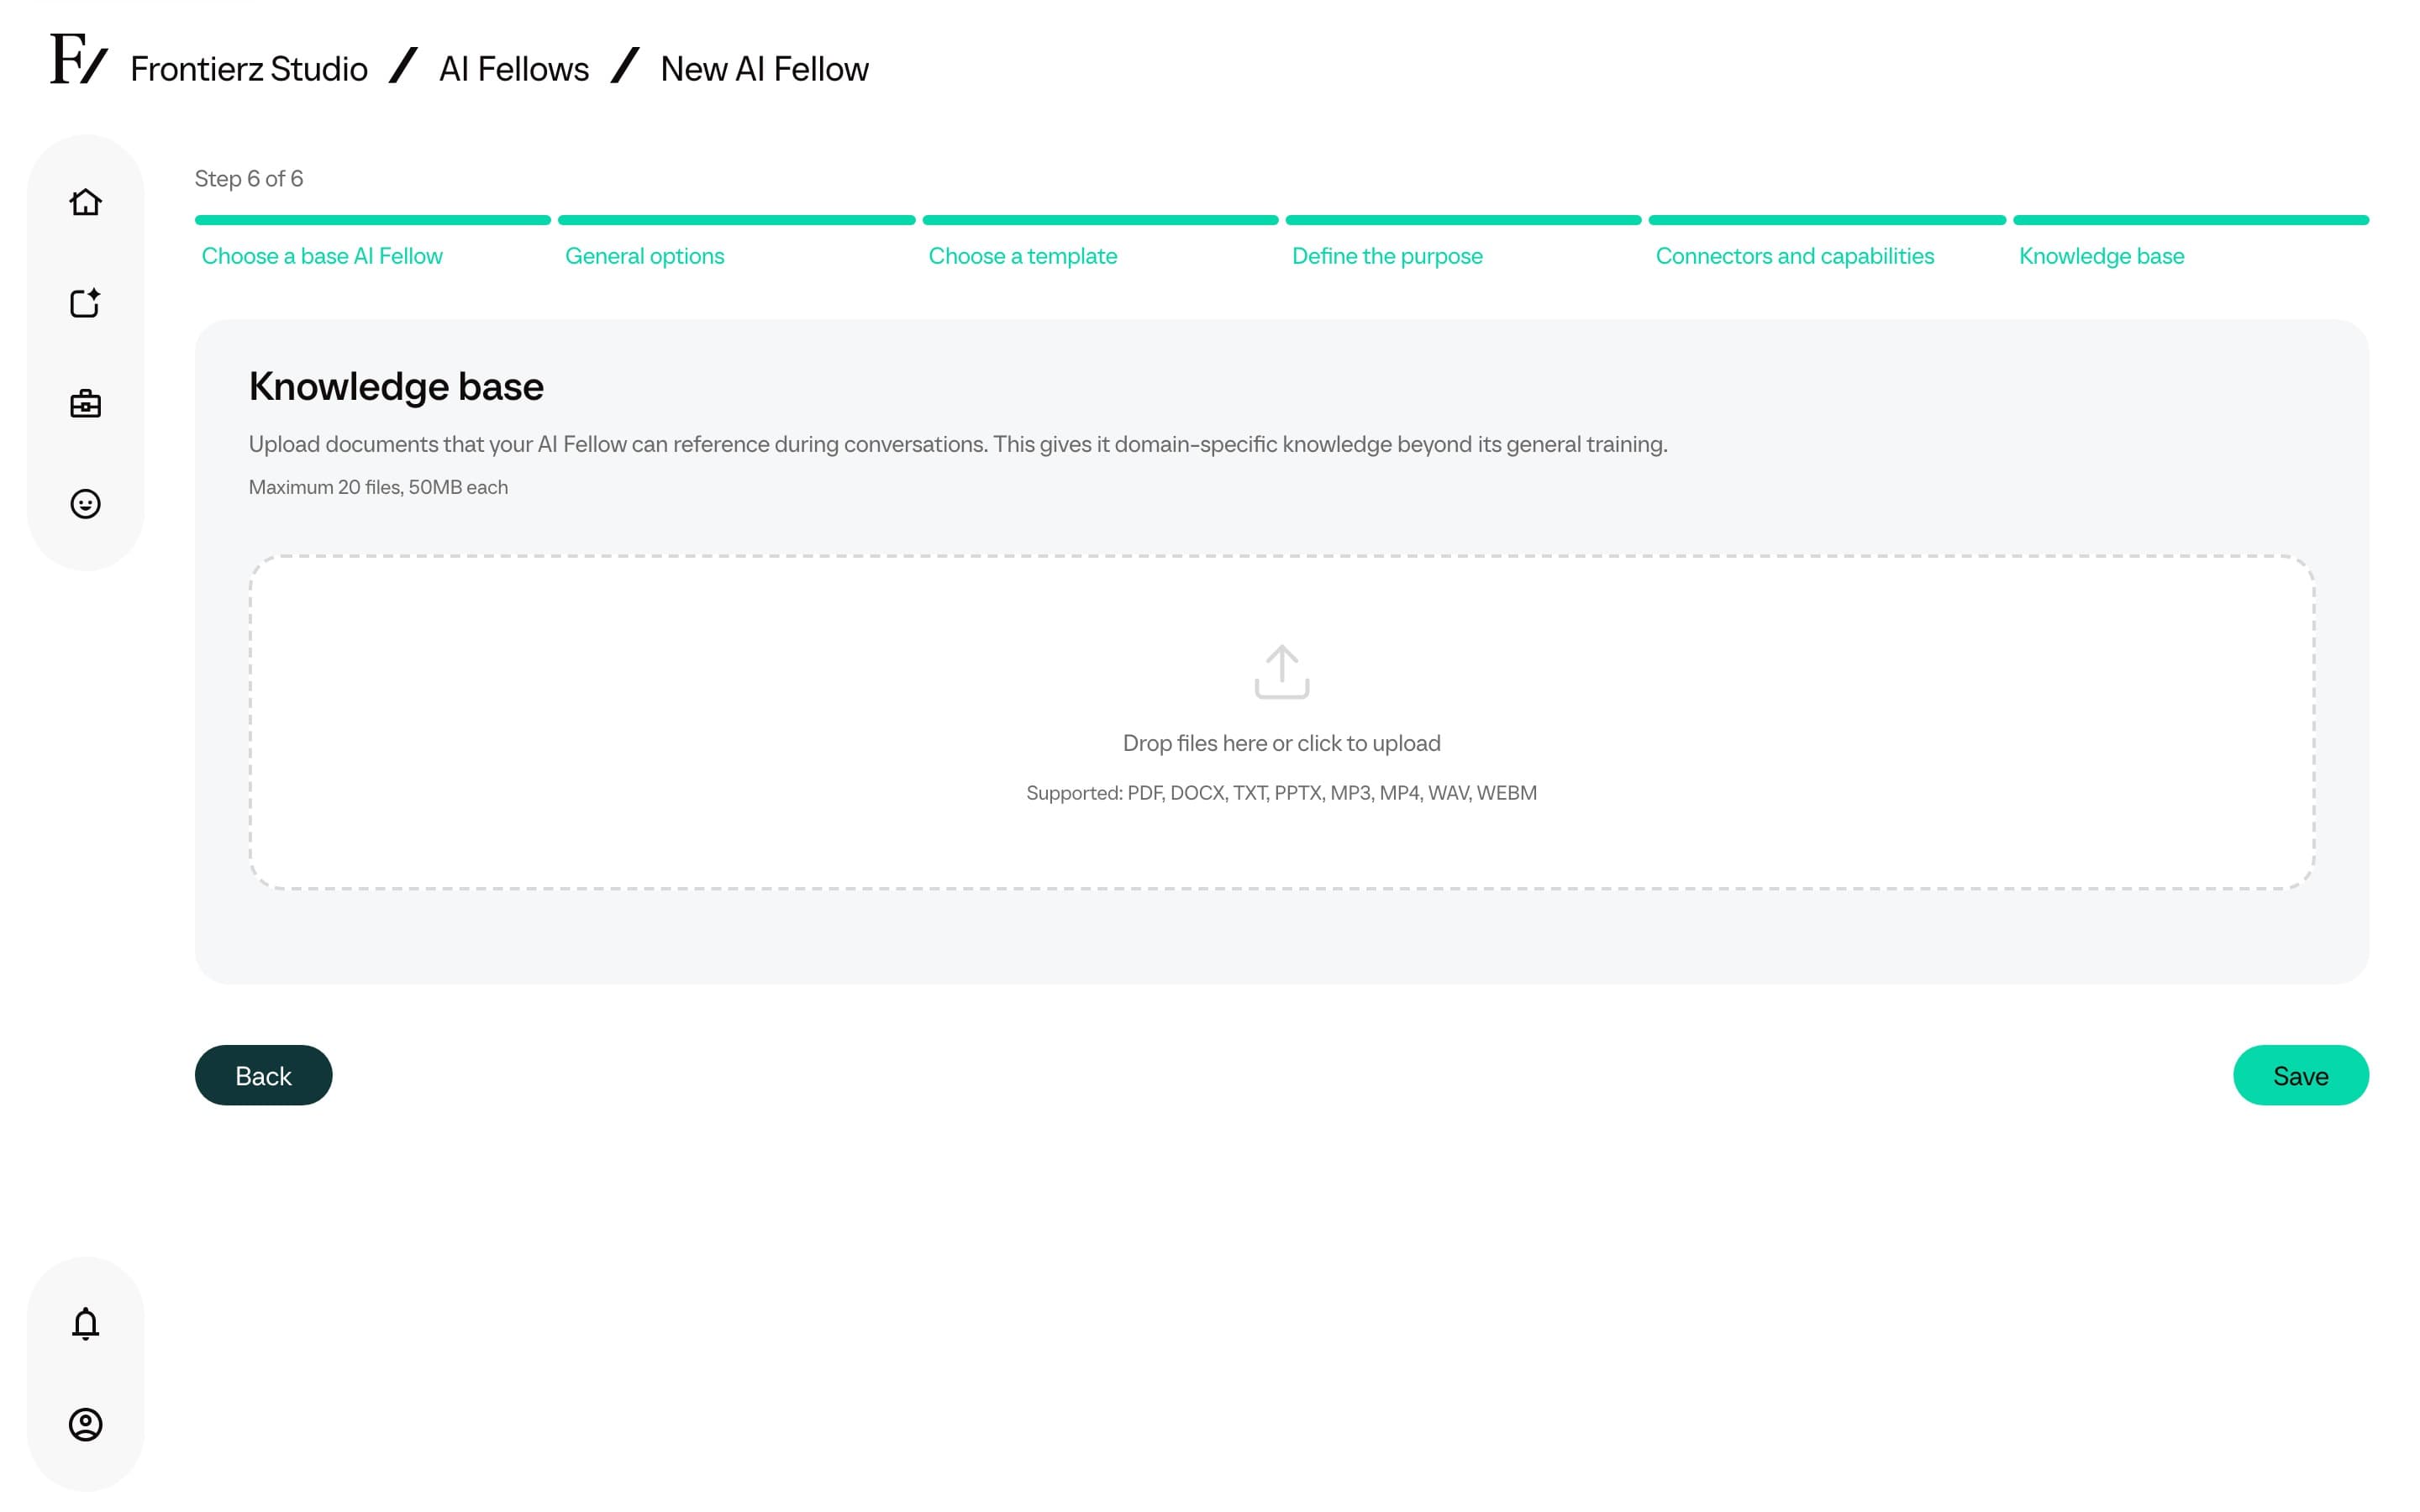
Knowledge Base files (PDFs, Word, PowerPoint, TXT, Markdown, audio, and video) are stored, processed, and used as reference material for the AI Fellow they were uploaded to.
- Full Admins, and Managers with access to that AI Fellow, can add, remove, or reprocess the files.
- During a conversation, the AI Fellow can search the processed knowledge and consult the relevant document for detailed answers. The search stays within that AI Fellow's Knowledge Base.
- A knowledge file can be deleted at any time. The AI Fellow updates its Knowledge Base after the change is processed.
Files sent during sessions
Users can send a file during an active AI Fellow session. The AI Fellow uses it as context for that conversation only. This does not add the file to the AI Fellow's Knowledge Base and does not change future sessions.
Supported files include images, PDFs, Word documents, PowerPoint decks, and text-like files. The transcript records that the user sent a file, using the file name.
For admin guidance, see Files sent during sessions.
Chat and whiteboard
What the AI Fellow shares during a session is handled differently depending on its type:
- Text the AI Fellow shares in Chat is saved with the conversation transcript, and users can copy it again from Previous chats.
- Images the AI Fellow creates are saved as image files so they can be shown and downloaded during the session.
- Whiteboard drawings, interactive widgets, and celebrations are session-only and are not kept after the call. Users can download a whiteboard as PNG or SVG.
Conversations and transcripts
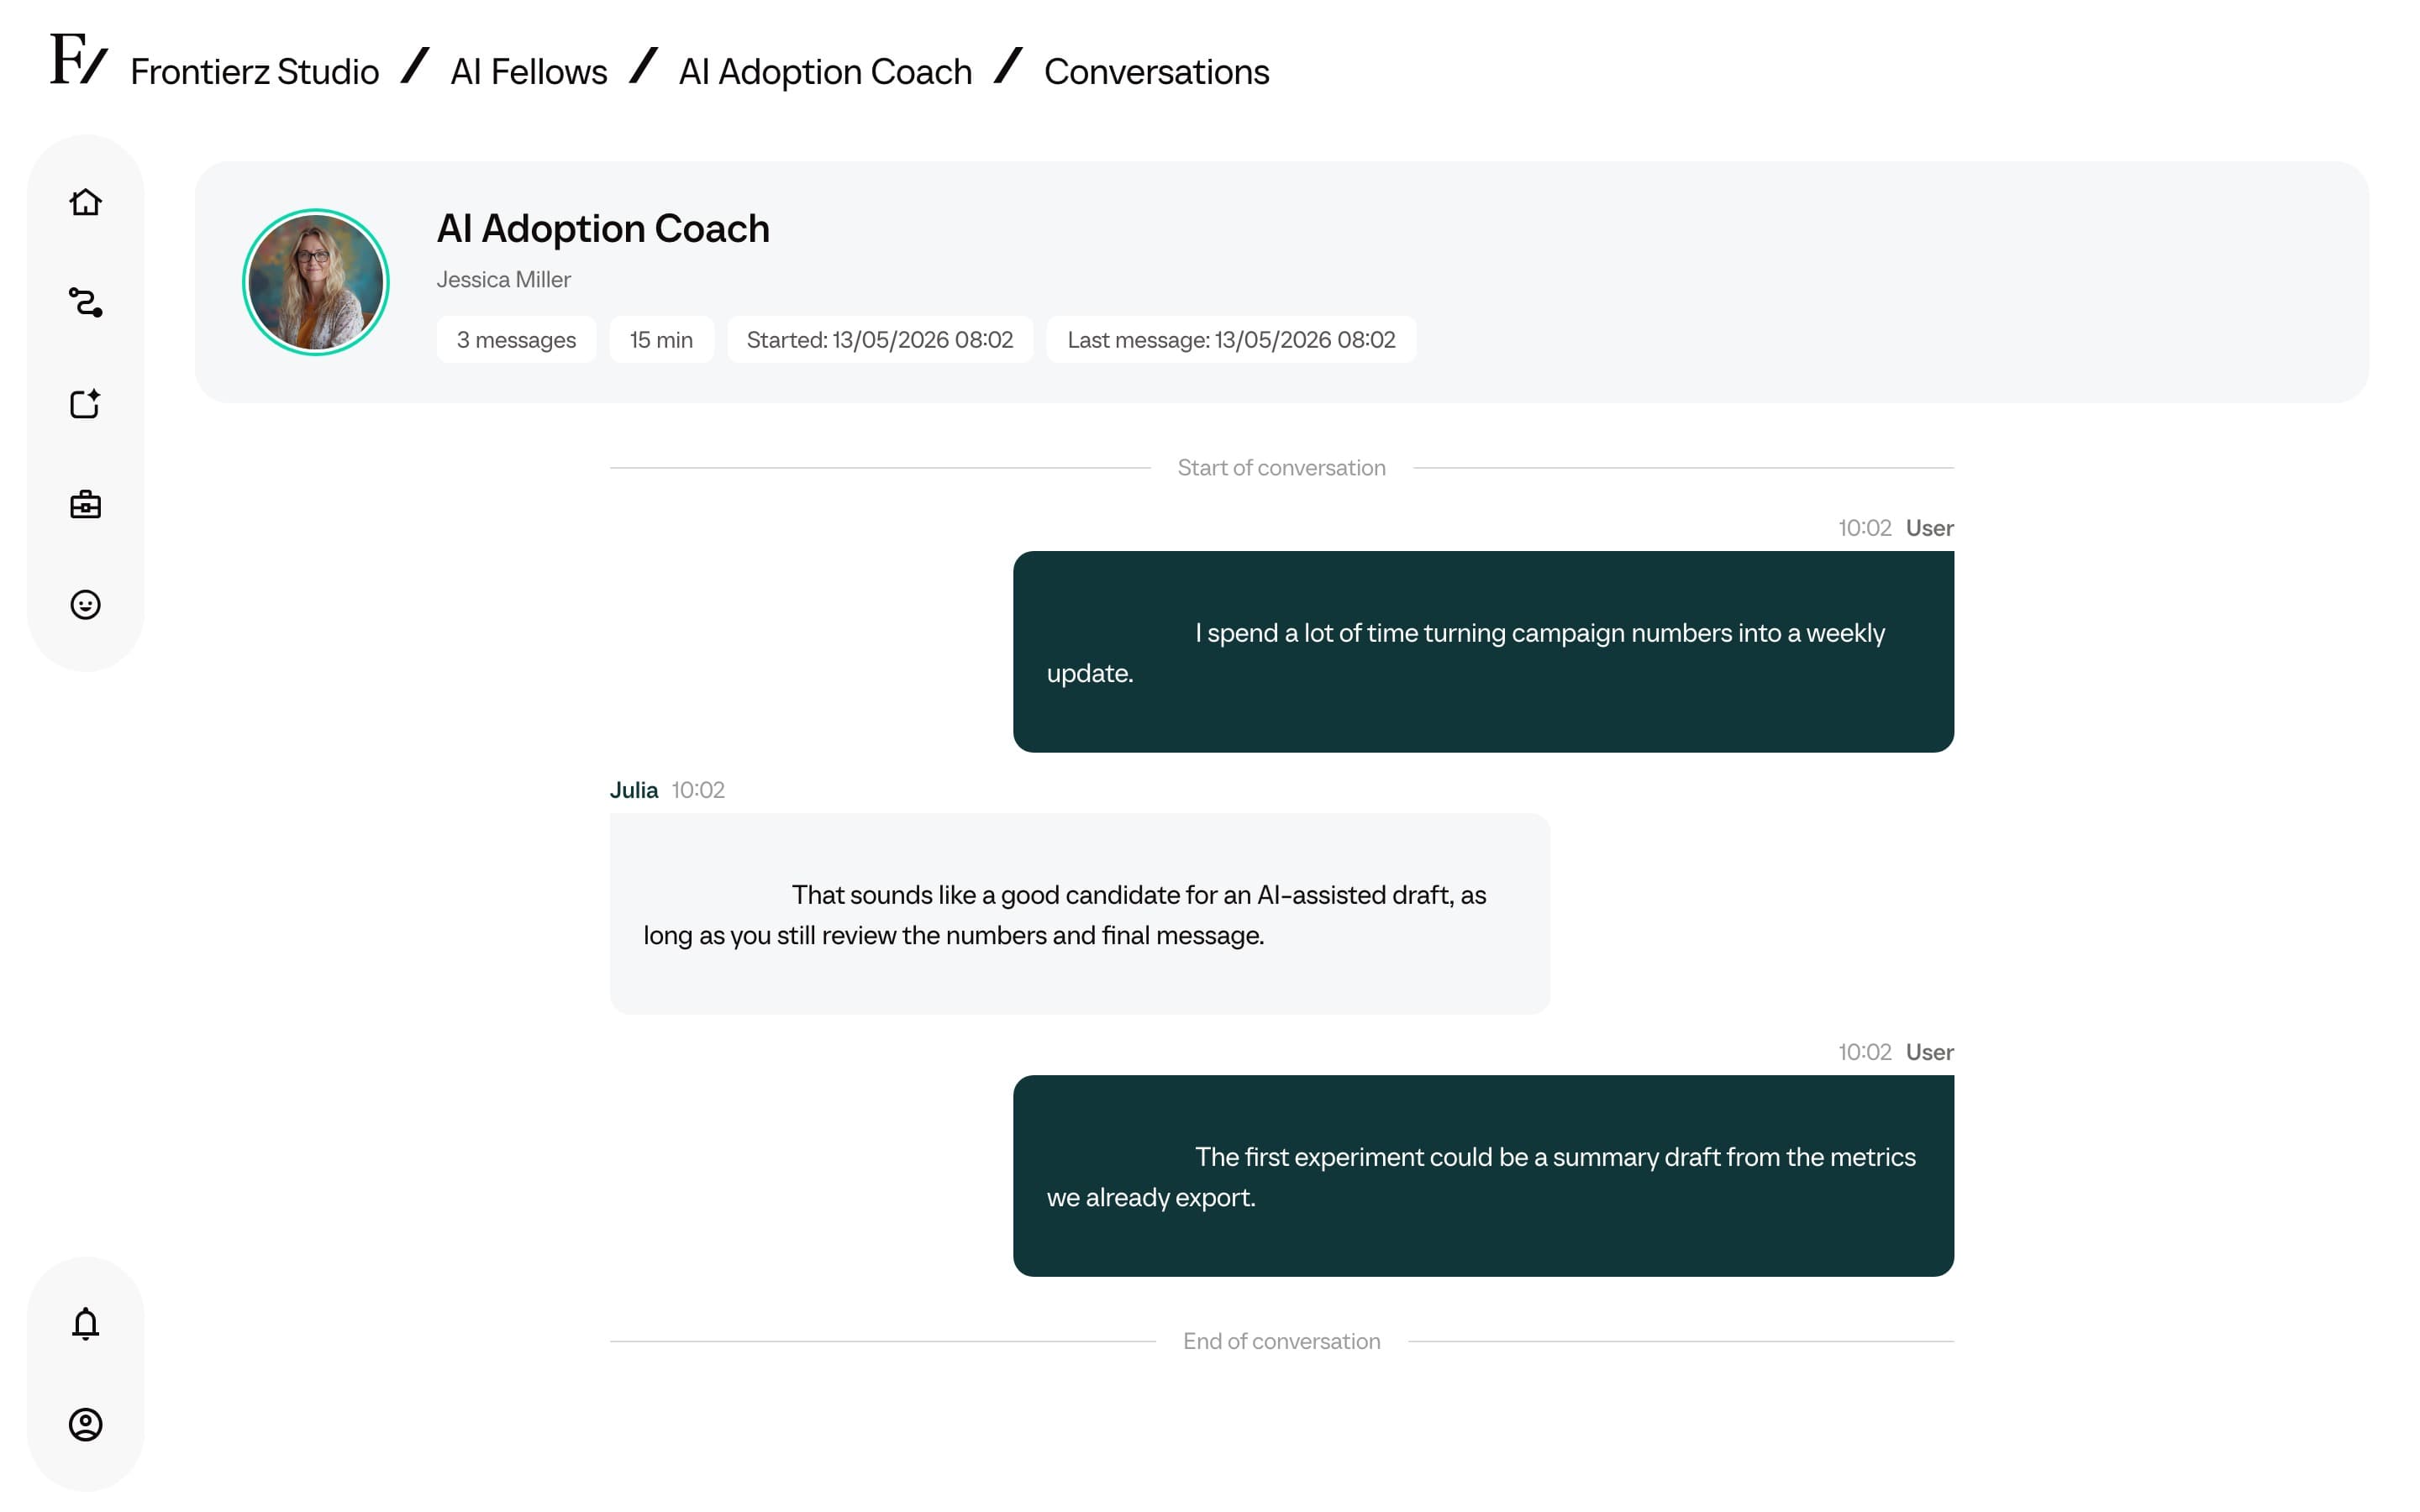
Live sessions are transcribed and summarized automatically.
- Administrators can review conversation history according to their role and the resources they have access to.
- Conversations on a Public AI Fellow are anonymous by default. The transcripts are visible to authorized administrators, but they are not attributed to a specific person unless the embed or link passes an external user ID.
- Conversations on a Private AI Fellow require login, so transcripts are attributed to the user who held them.
- Conversations inside a Learning Path are tied to the enrolled user for progress purposes; authorized administrators can see who completed which session and when.
Camera sharing
Camera sharing is disabled by default. The user must explicitly enable the camera and can disable it at any time during a session. While the camera is on, the AI Fellow takes a camera snapshot only when the user asks it to look, rather than receiving a continuous video stream. Camera data is not retained beyond the active session.
See AI Fellows for the live-session details.
Screen sharing
Screen sharing is disabled by default. The user selects the screen, window, or tab to share through the browser's dialog and can stop sharing at any time. The AI Fellow only sees what was explicitly shared. What was shared is not recorded or kept after the session.
Connector data
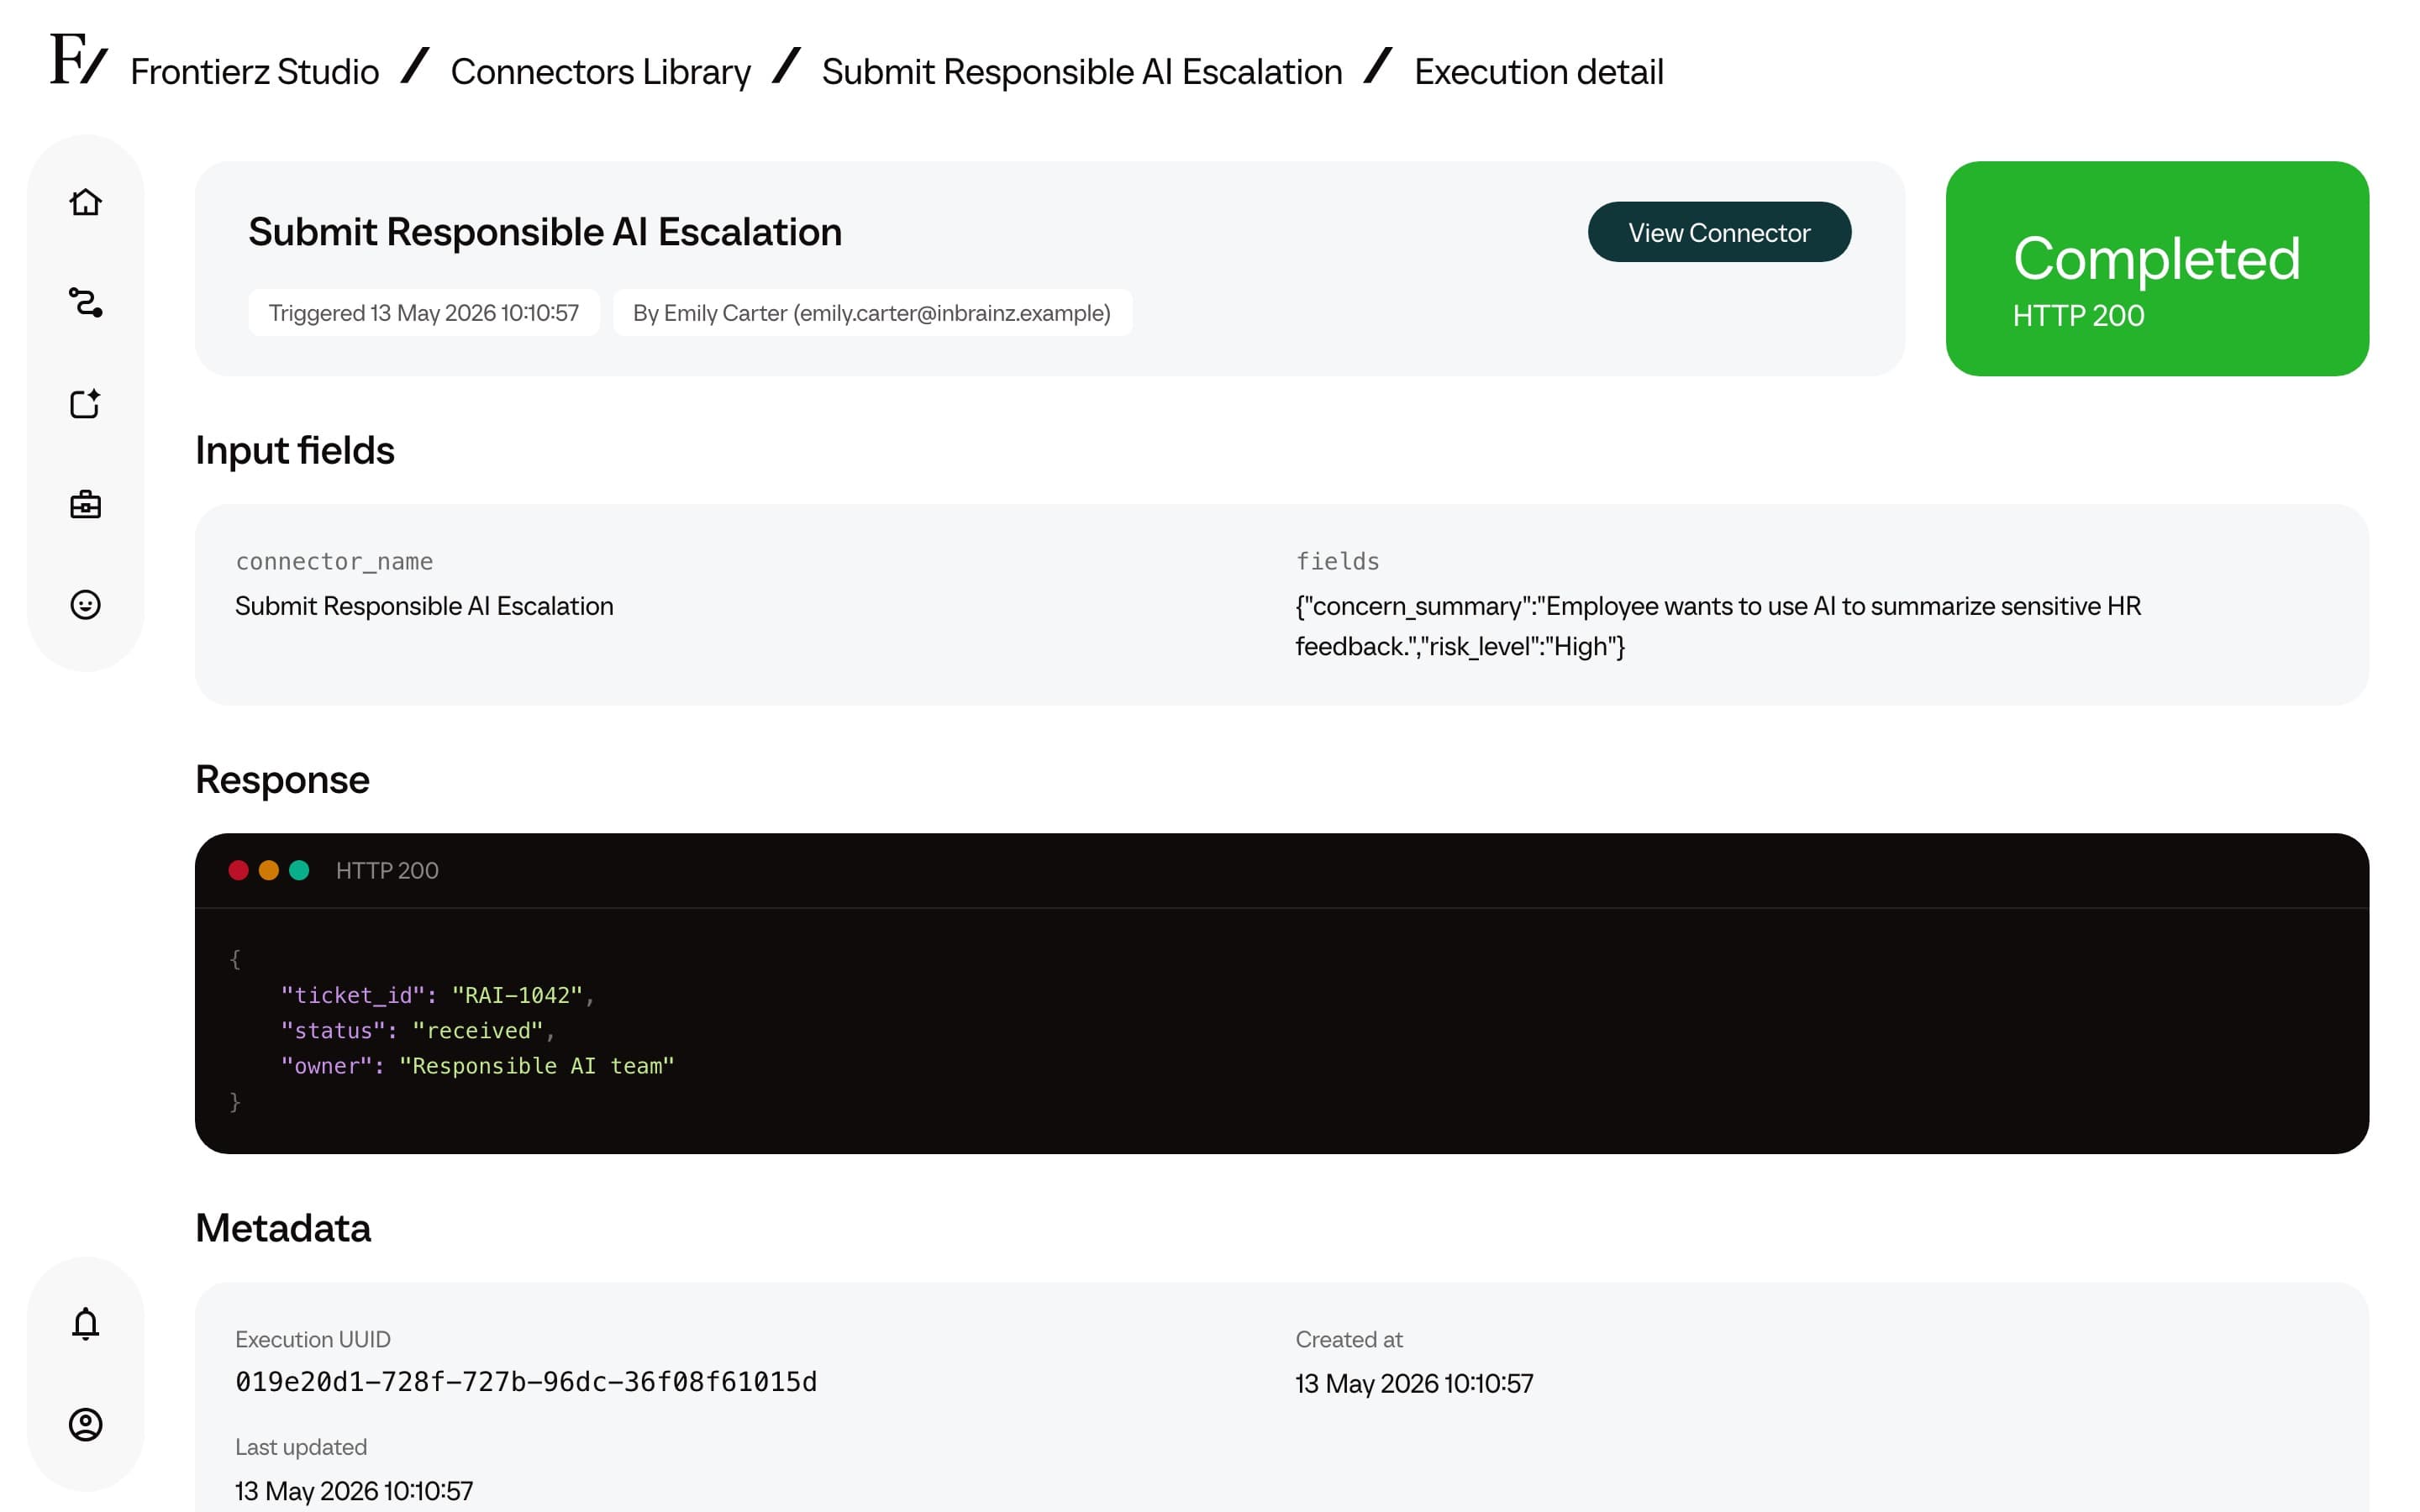
When a Connector is invoked, the data the AI Fellow gathered from the user is sent to the system the Connector points to (such as a CRM, LMS, HR system, or any other system configured by the customer's IT team). Frontierz logs the request and the response on its side for audit purposes. What the receiving system does with the data depends on that system's own retention and processing rules.
A Webhook Connector can also send the signed-in person's name and email
address when its request body uses the {{user.name}} or
{{user.email}} placeholders. Frontierz takes these from the account,
so Anonymize personal data does not remove them. Guests without an
account send empty values. See
Include the user's name and email.
Company isolation
Each Frontierz customer operates inside its own logical company account. Data from one company is not visible to other customers. The platform enforces access controls on the server side, so security does not depend on hiding menu items.
Anonymize personal data
When Anonymize personal data is on for an AI Fellow, a model on the user's device replaces names, email addresses, phone numbers, addresses, and IDs with placeholders before the conversation is stored. Stored transcripts contain those placeholders, such as [EMAIL_1], instead of the original details. In text chat, the AI Fellow also sees only the placeholders. The user still sees the original details on their own screen. A shield on a message means personal details in that turn were masked on the device.
This does not cover voice audio, files, the camera, or screen sharing. It catches most personal data, not every case. On a Private AI Fellow or a Learning Path, the conversation remains tied to the signed-in user.
During the session the user sees Setting up private mode, Private mode is on, or Private mode is not working. If private mode is not working, typed messages are not sent and the conversation is not saved, but speech still reaches the AI provider. The user can select Try again.
The setting is under Capabilities, in Session flow. See Connectors.
Activity Log
Owners and Full Admins can review administrative changes in Company Settings → Activity Log. The log shows who changed Learning Paths, AI Fellows, roles, access, and company settings. It does not list learning progress or a person's account profile. Passwords and secrets are not shown. See Activity Log. How long these records are kept depends on your agreement.
Items to confirm with the Frontierz account team
Confirm the following details with your Frontierz account team before making commitments to colleagues or external parties. The applicable terms depend on your agreement, region, and configuration.
- Data residency options (where data is physically hosted).
- Encryption details (algorithms, key management).
- Retention policies (how long transcripts and analytics are kept).
- Deletion policies (what happens when data is deleted, and how long it takes to fully purge).
- Subprocessor list (third parties that touch customer data).
- How long Activity Log records are kept.
- SSO and identity provider support.